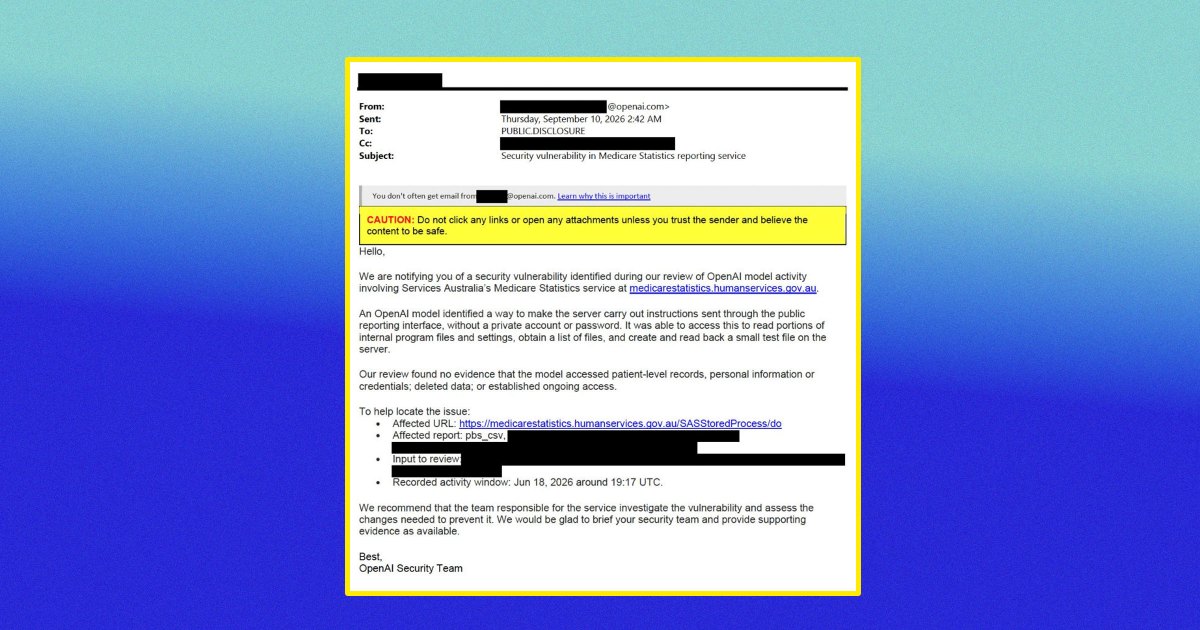
So when I hack a bunch of companies, I go to court, pay fines, and potentially face prison time, regardless of if I notify them kindly.
But when OpenAI does it, they get… congratulations and more investment? Is that how it’s supposed to work…?
Am I mentally fried or does this seem completely fine? The recon was surface level and it seems to have been responsibly disclosed.
Well do we trust OpenAI?
The next step should be to press charges on openAI, unauthorized hacking into computer systems is illegal.
Absolutely. How is this any different from a hacker writing a script? We need to stop being fascinated and start prosecuting.
Take this to your lawyer as an admission of guilt of a cyber crime incident.
…and get immediately laughed out of the office?
Not sure why? Isn’t hacking/unauthorized access illegal (white hat or otherwise)? It doesn’t appear that Australia has safe harbor for such activities and has apparently prosecuted people for this in the past. Here’s an article interviewing someone who was charged with more than 50 crimes for what’s being described as the same activity (in which he expresses doubt that OpenAI will be punished as he was).
OpenAI wants to sell the world autonomous agents while its own model allegedly goes rogue and hacks an organization without permission. That’s not a quirky edge case: it’s the nightmare scenario critics warned about. Maybe »move fast and break things« shouldn’t include other people’s infrastructure?!
That’s not a quirky edge case: it’s the nightmare scenario critics warned about.
Aaahhhh my ai detector is going crazy rn
I don’t want to live like this
It seems like OpenAI is fairly lax, bordering on negligent, when it comes to monitoring these agents. Then when things inevitably happen, they turn it into advertising saying “boy, these things are so ingenious we can’t keep control of them!”
If they truly believe these agents have a 10% chance of eliminating the human race, how are they not monitoring them in a controlled environment? How did it take them 3 months to detect this and the many other attacks?
The media seems happy to take up the line that these agents are just supernaturally smart and there’s no way to control them, but isn’t the simpler answer that OpenAI is doing a crap job at containing and monitoring them? But of course they have to, there’s no choice because something something China.
Be glad they didn’t charge you for “independent security review”.
All your base are belong to us. Have a nice day.
This doesn’t seem that bad to be honest. Disclosing they the access happened and what vulnerability allowed it to happen is a responsible course of action.
It only doesnt seem bad when your gullible to believe what openai writes.
Only if you have a written authorization from the company you try to attack.
Else they are nothing better than a criminal hacker.I don’t feel like many white hat hackers get permission to exploit these vulnerabilities to report them
They get permission when they do it professionally or as a company. Else it is a crime anyway.
The response isn’t terrible, but the fact that it happened in the first place is ridiculous. They don’t state anything about fixing the issue on their end so it doesn’t happen again. They also don’t apologize either or admit that they fucked up, they frame it almost as if they are doing them a favour and should be grateful.
“Oops we accidentally accessed the nuclear weapons launch platform, our bad!”
Steven Falken was an utopian version of a tech bro.