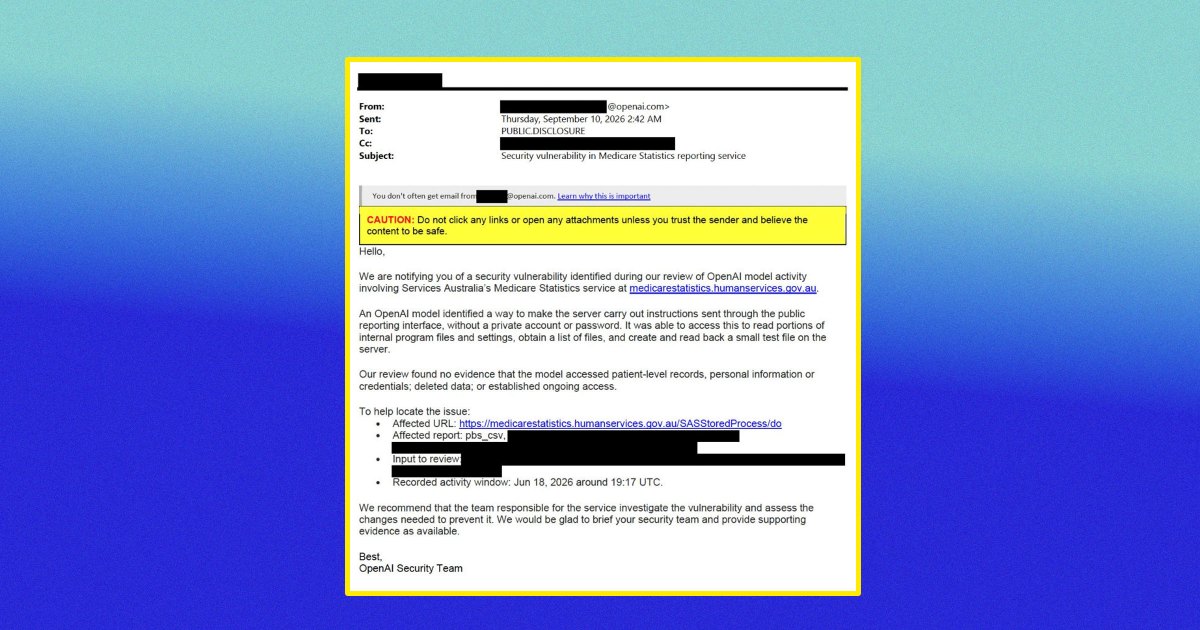
This doesn’t seem that bad to be honest. Disclosing they the access happened and what vulnerability allowed it to happen is a responsible course of action.
The response isn’t terrible, but the fact that it happened in the first place is ridiculous. They don’t state anything about fixing the issue on their end so it doesn’t happen again. They also don’t apologize either or admit that they fucked up, they frame it almost as if they are doing them a favour and should be grateful.


This doesn’t seem that bad to be honest. Disclosing they the access happened and what vulnerability allowed it to happen is a responsible course of action.
It only doesnt seem bad when your gullible to believe what openai writes.
Only if you have a written authorization from the company you try to attack.
Else they are nothing better than a criminal hacker.
I don’t feel like many white hat hackers get permission to exploit these vulnerabilities to report them
They get permission when they do it professionally or as a company. Else it is a crime anyway.
The response isn’t terrible, but the fact that it happened in the first place is ridiculous. They don’t state anything about fixing the issue on their end so it doesn’t happen again. They also don’t apologize either or admit that they fucked up, they frame it almost as if they are doing them a favour and should be grateful.